Survey Says…. Remote Code Execution: CVE-2026-90817
A double-decoding flaw exposed REDCap's Data Import controller to public survey users. A client-controlled PHP stream then turned CSV BOM cleanup into a Blade cache overwrite and unauthenticated RCE.
One Login, Two RCEs: CVE-2026-90822 and CVE-2026-90823
A stack overflow in FatPipe's privileged authentication helper looked like the hard path to root. Tracing its web reachability exposed a second flaw in the middle: unauthenticated command injection in xtremed.
CVSS Is Not A Negotiation
CVSS scoring disputes often come down to mixing intrinsic vulnerability severity with deployment assumptions, exploit-development effort, remediation pressure, and bounty economics. This guide explains how to keep those factors in the right metrics.
File Drop to RCE – CVE-2026-20217
I remember watching Simon Scannell's REcon 2023 talk, [...]
The Rise Of Offensive AI
Unless you've been living under a rock, you're [...]
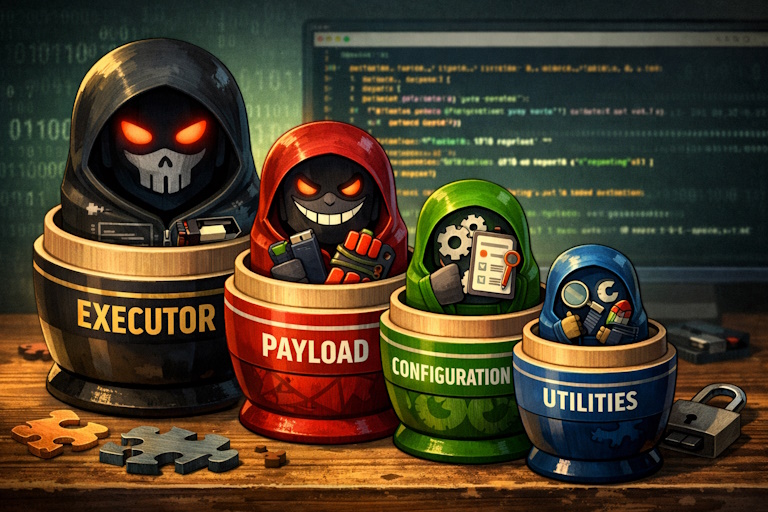
Python Dependency Confusion All the Way Down
With the recent LiteLLM supply chain compromise making headlines, we wanted to take a deep dive into how an advanced attacker can go far beyond a basic dependency confusion attack against modern technology companies — and what defenders should be looking for.
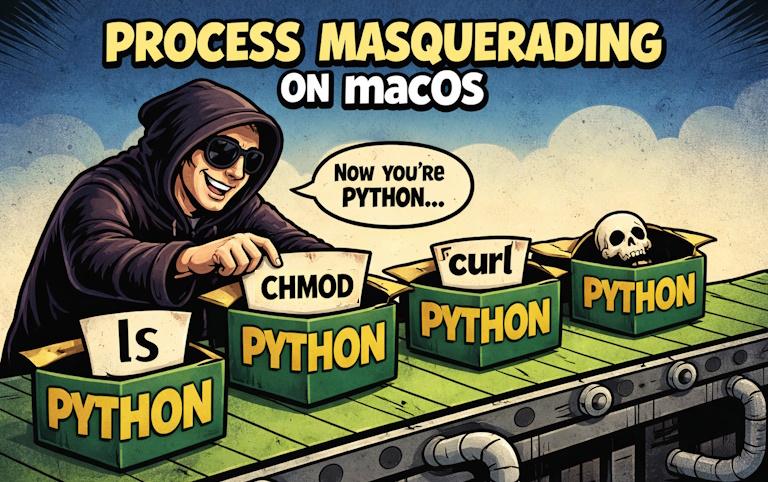
Process Masquerading on macOS
In a previous post we documented how we used [...]
Reverge AI Assistant Now Powered by Goose
We're excited to share that Reverge 1.2.0 is out. [...]